DORA does not forgive
a fragmented vendor stack.
One vendor you forgot to patch is now something a regulator can point to by name.
Twigex brings your data, files, chat, and reporting into one self-hosted platform. That means one system to secure and defend at audit, not a dozen.
What's actually going wrong today.
DORA is a new EU rule that makes financial firms track and justify every outside tech vendor they use, and in 2026 regulators started actively enforcing it. Every SaaS tool in your stack is one more vendor you now have to account for.
Client financial data, models, and messages spread across a dozen cloud and reporting tools multiply the exact kind of vendor risk DORA was written to reduce.
Firms getting ready for an audit, investor due diligence, or an IPO need trustworthy, consolidated numbers on demand, not days spent manually reconciling disconnected systems.
Built for how finance teams actually work.
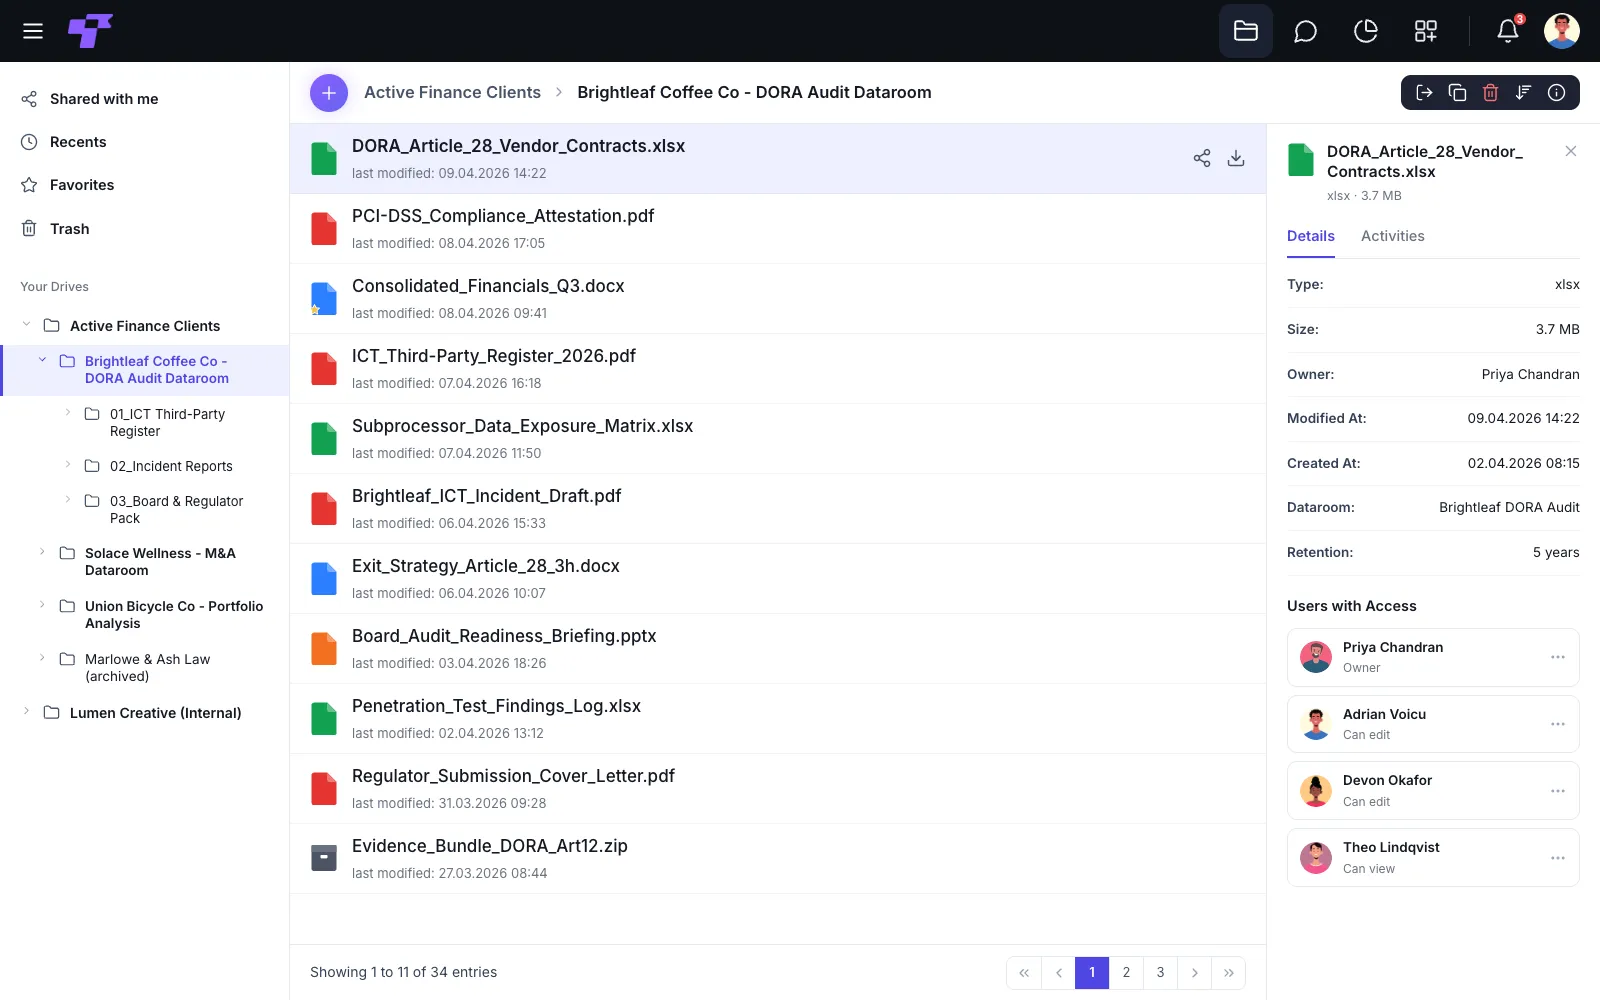
Vendor contracts, compliance attestations, and the ICT third-party register live in one access-controlled dataroom, not scattered across a dozen vendor logins.
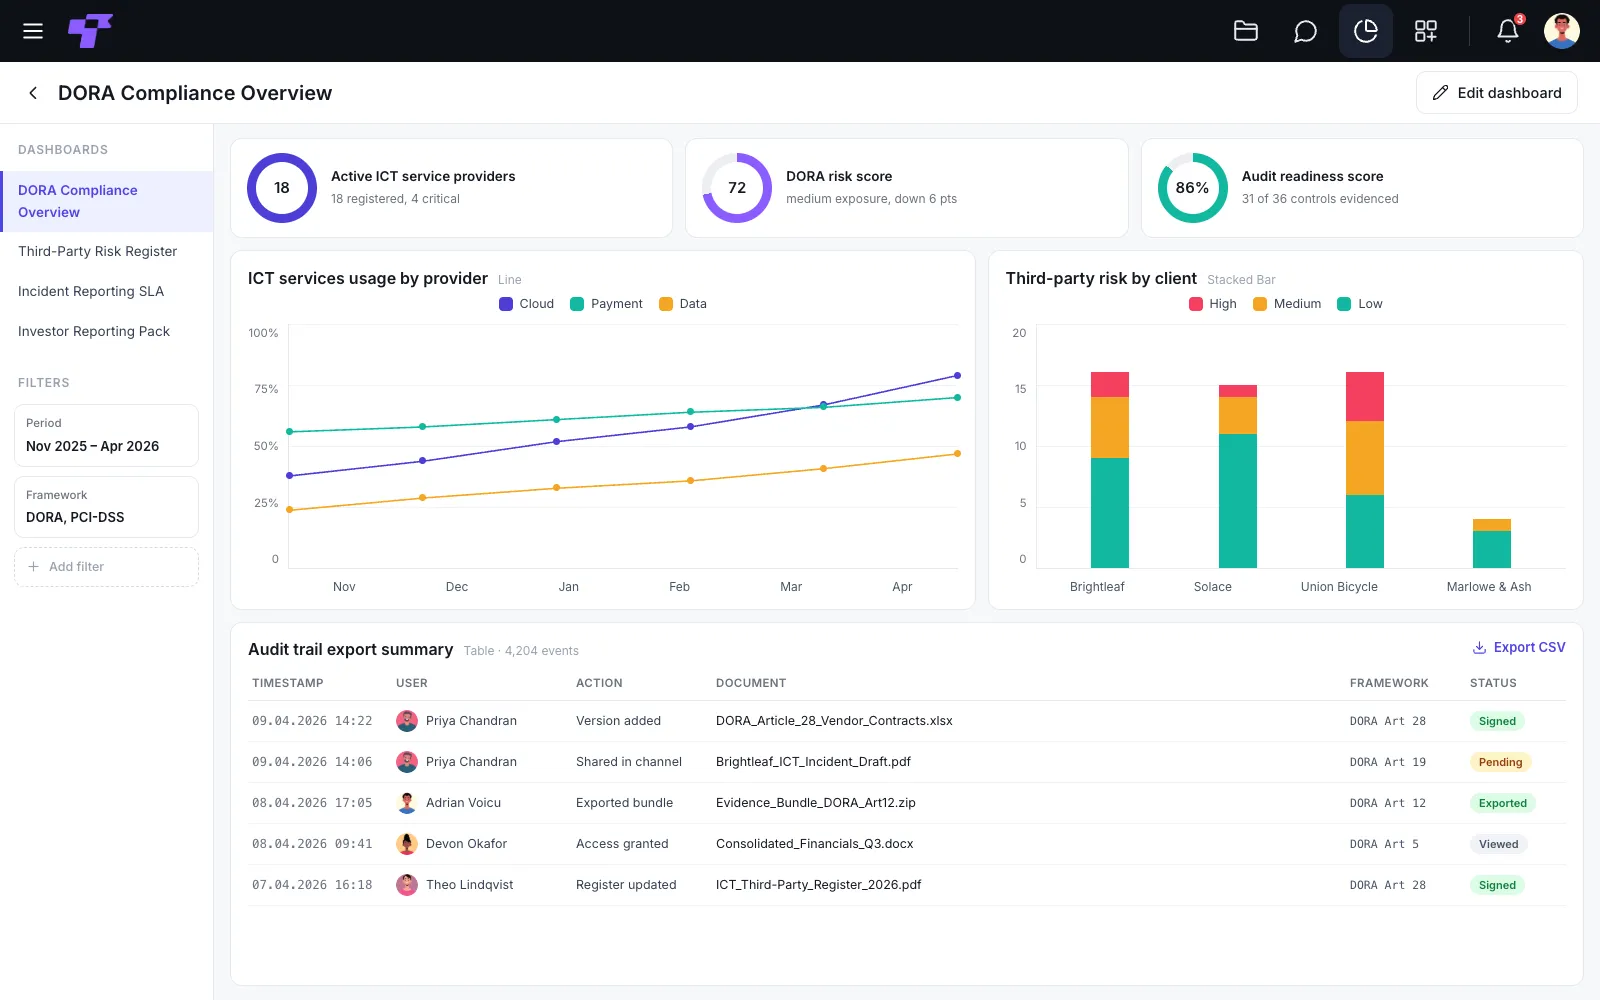
A live DORA risk score and audit readiness score, not a number your team reconstructs by hand the week before a regulator visit.
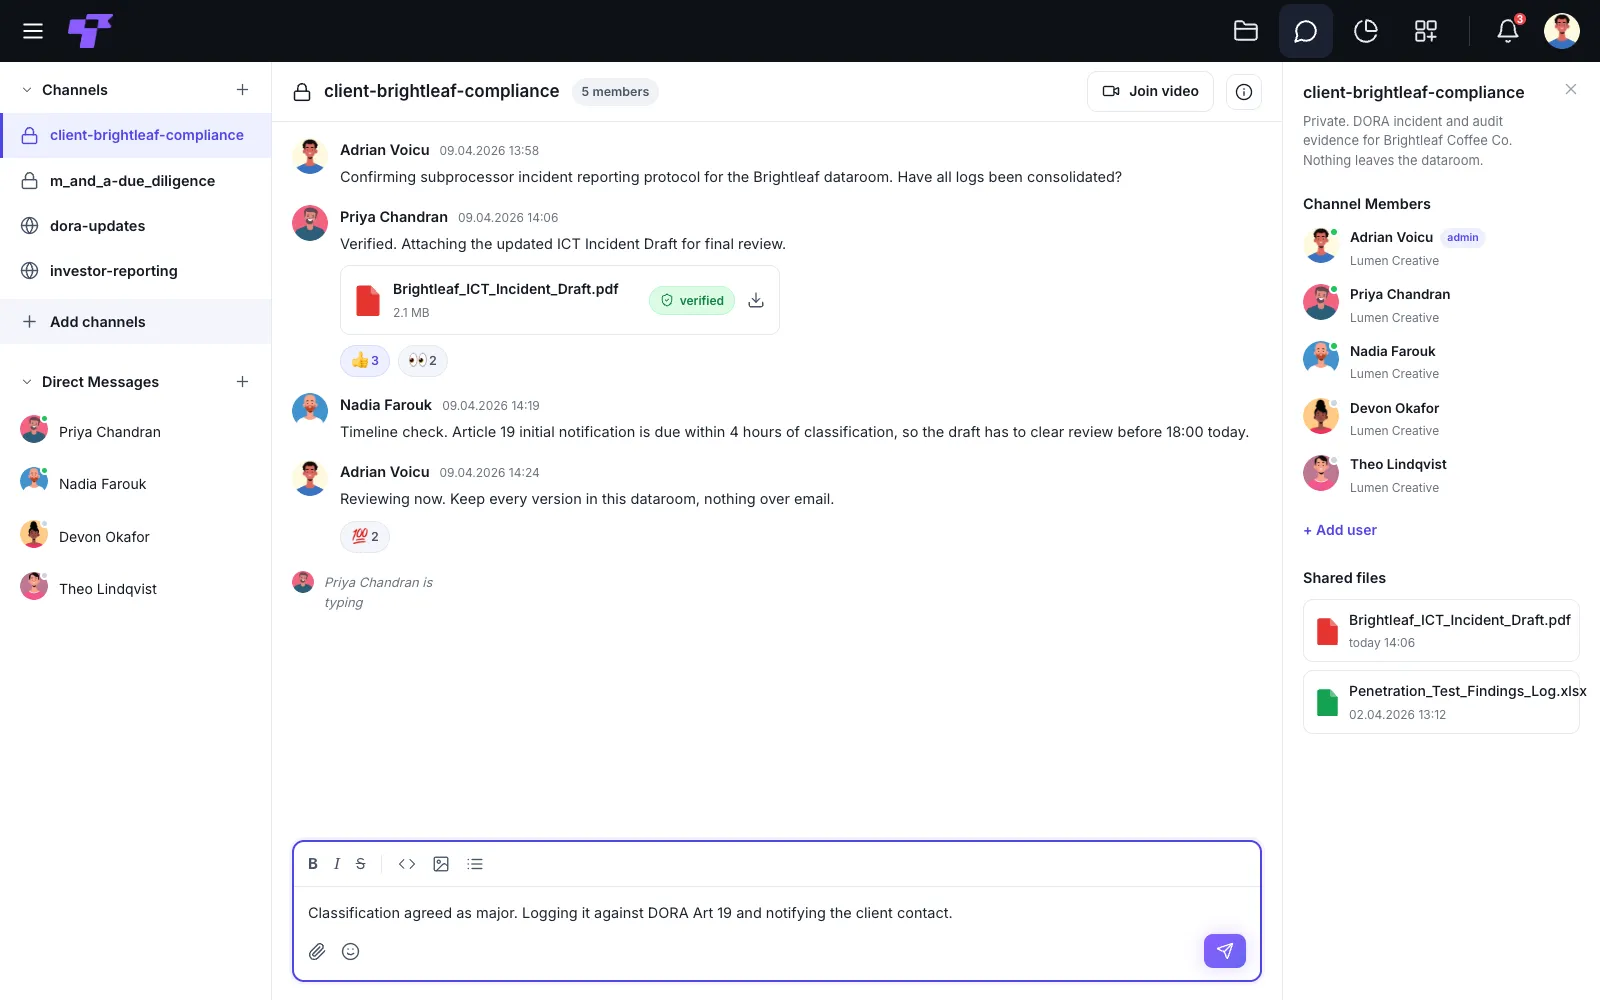
Incident classification and notification decisions happen in the same private channel that becomes the audit record, timestamped and never over email.
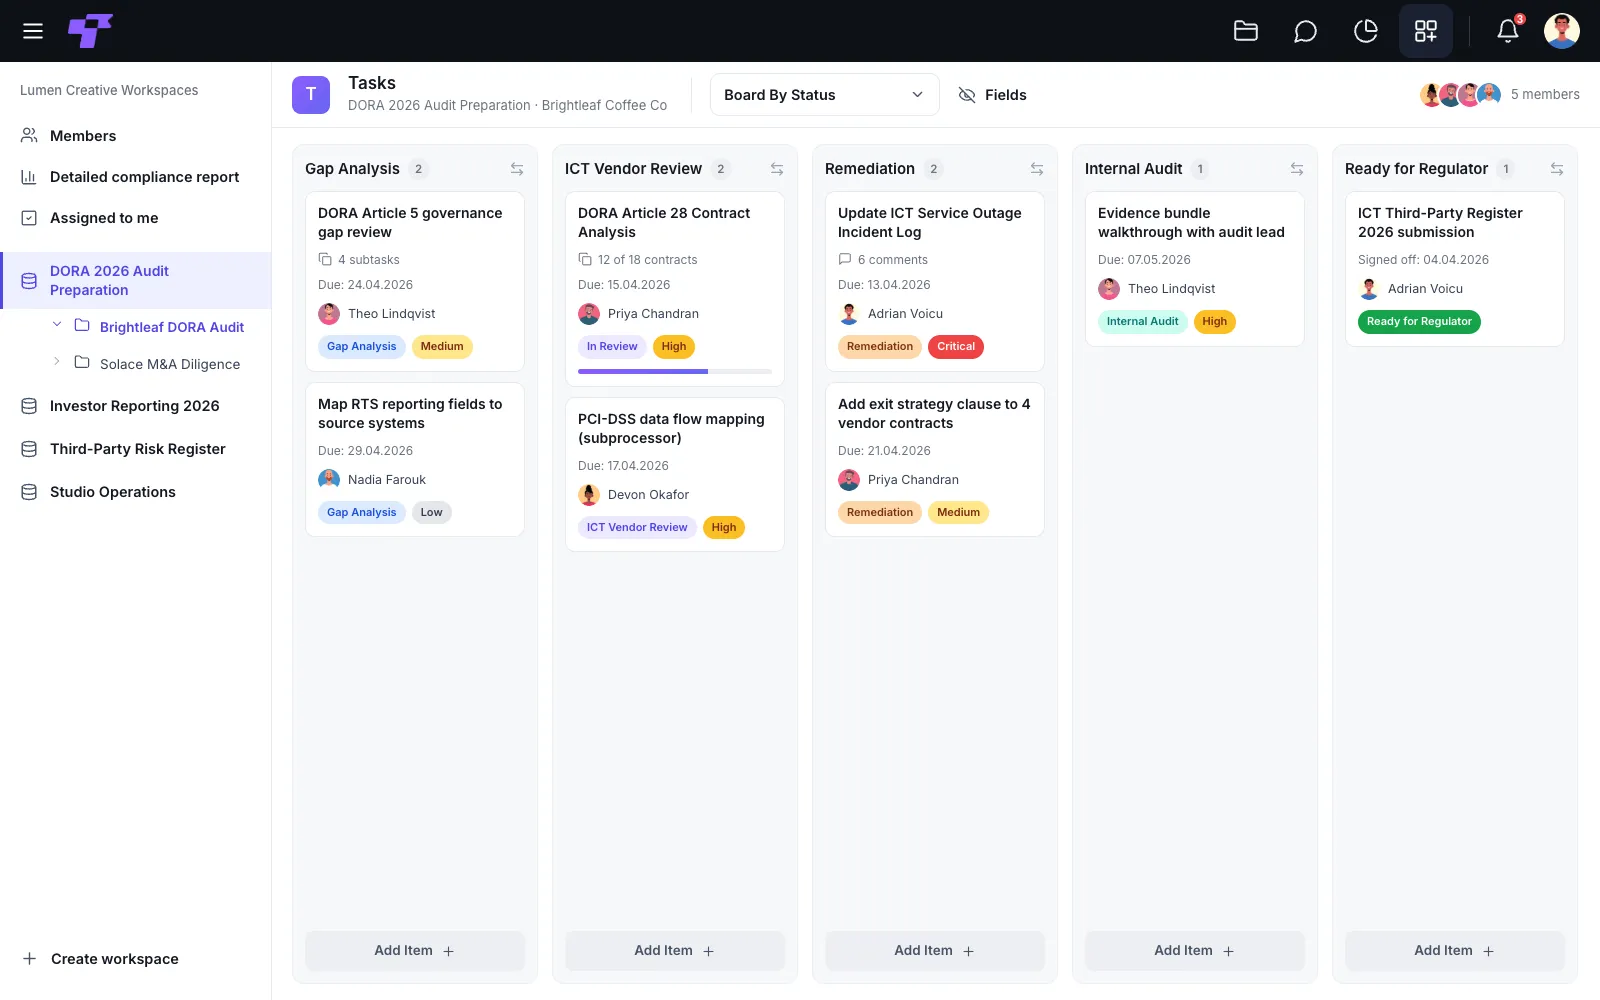
Every remediation task, from first gap analysis to final regulator sign-off, tracked on one board your audit lead actually trusts.
DORA's 2026 enforcement is already flagging gaps in firms' vendor registers and reporting. The fastest fix is having fewer vendors to register in the first place.
Here's how Twigex fixes it.
See it working in your sector.
Talk to our team about your specific compliance requirements and deployment constraints.