Care decisions need
cited evidence, not black boxes.
A clinician should never have to choose between asking AI for an answer and knowing where that answer came from.
Twigex keeps patient health information inside your own infrastructure at all times. None of it ever reaches an outside AI provider, and every record stays traceable back to where it came from.
What's actually going wrong today.
Patient records, scans, referral letters, and clinical notes are scattered across different medical record systems, shared drives, and messaging apps. None of it can safely be fed into AI without risking a HIPAA violation or exposing patient data.
Every integration with a public AI tool raises the same unanswered question for compliance teams: where does the patient data actually go, and who else can see it?
Clinicians lose real time hunting for information across disconnected systems, time that, for a patient, can mean the difference in outcome, not just a productivity number.
Built for how medicine teams actually work.
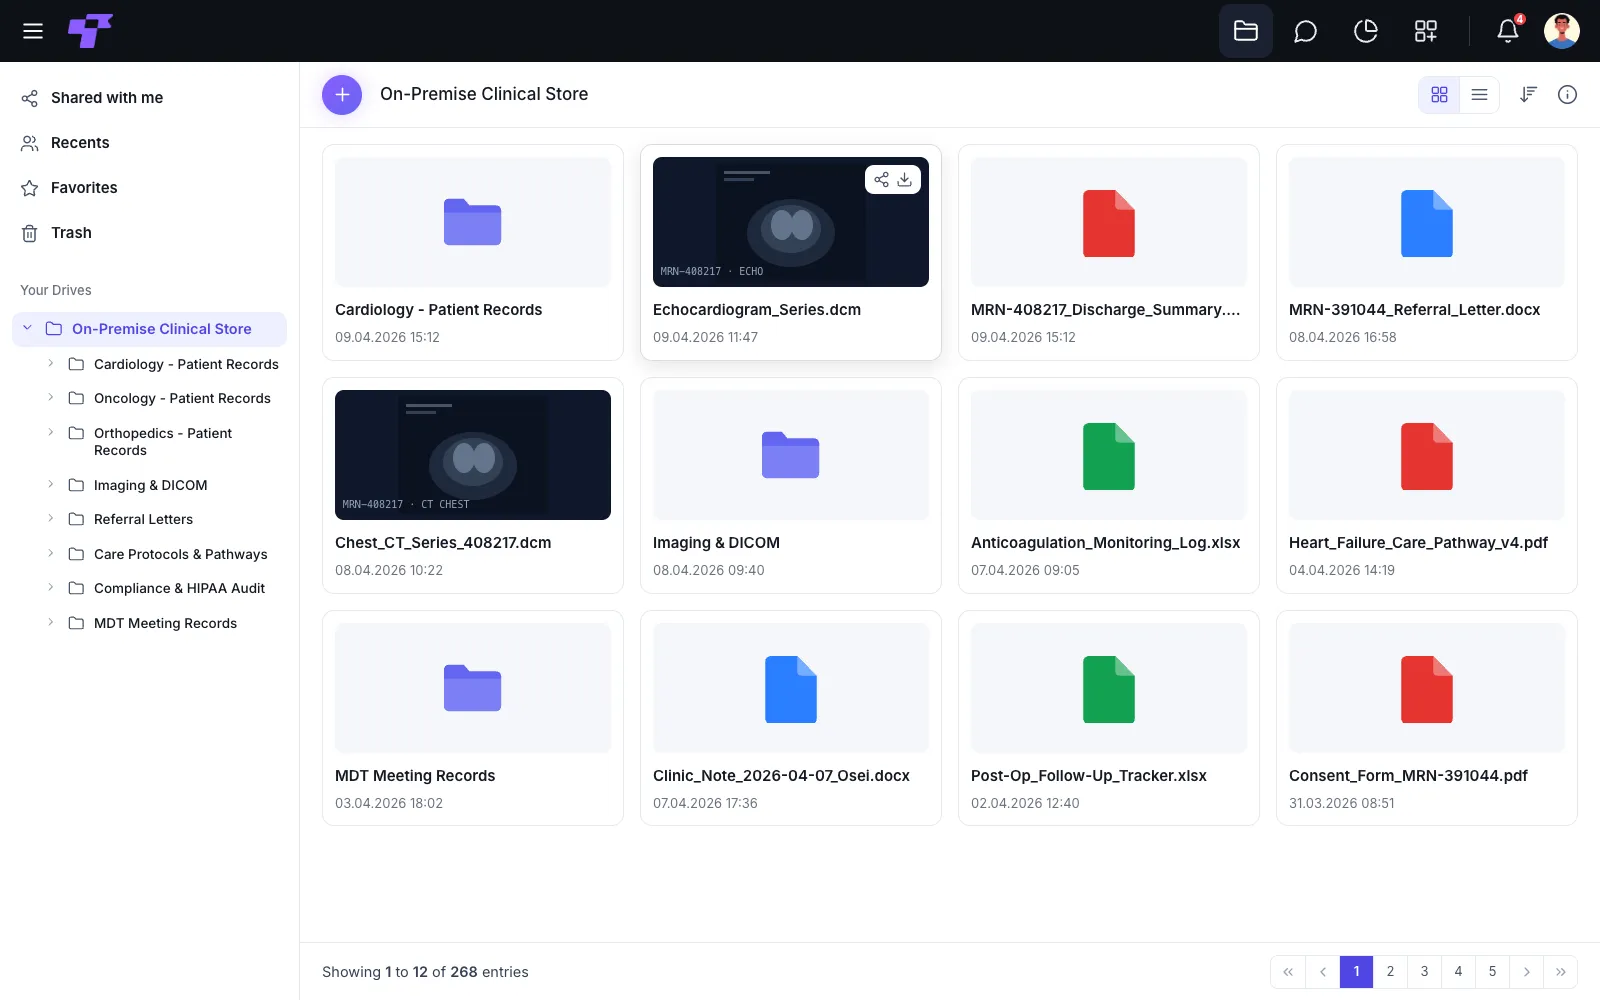
Patient records, imaging, and referral letters live in one on-premise store, not scattered across different record systems and shared drives.
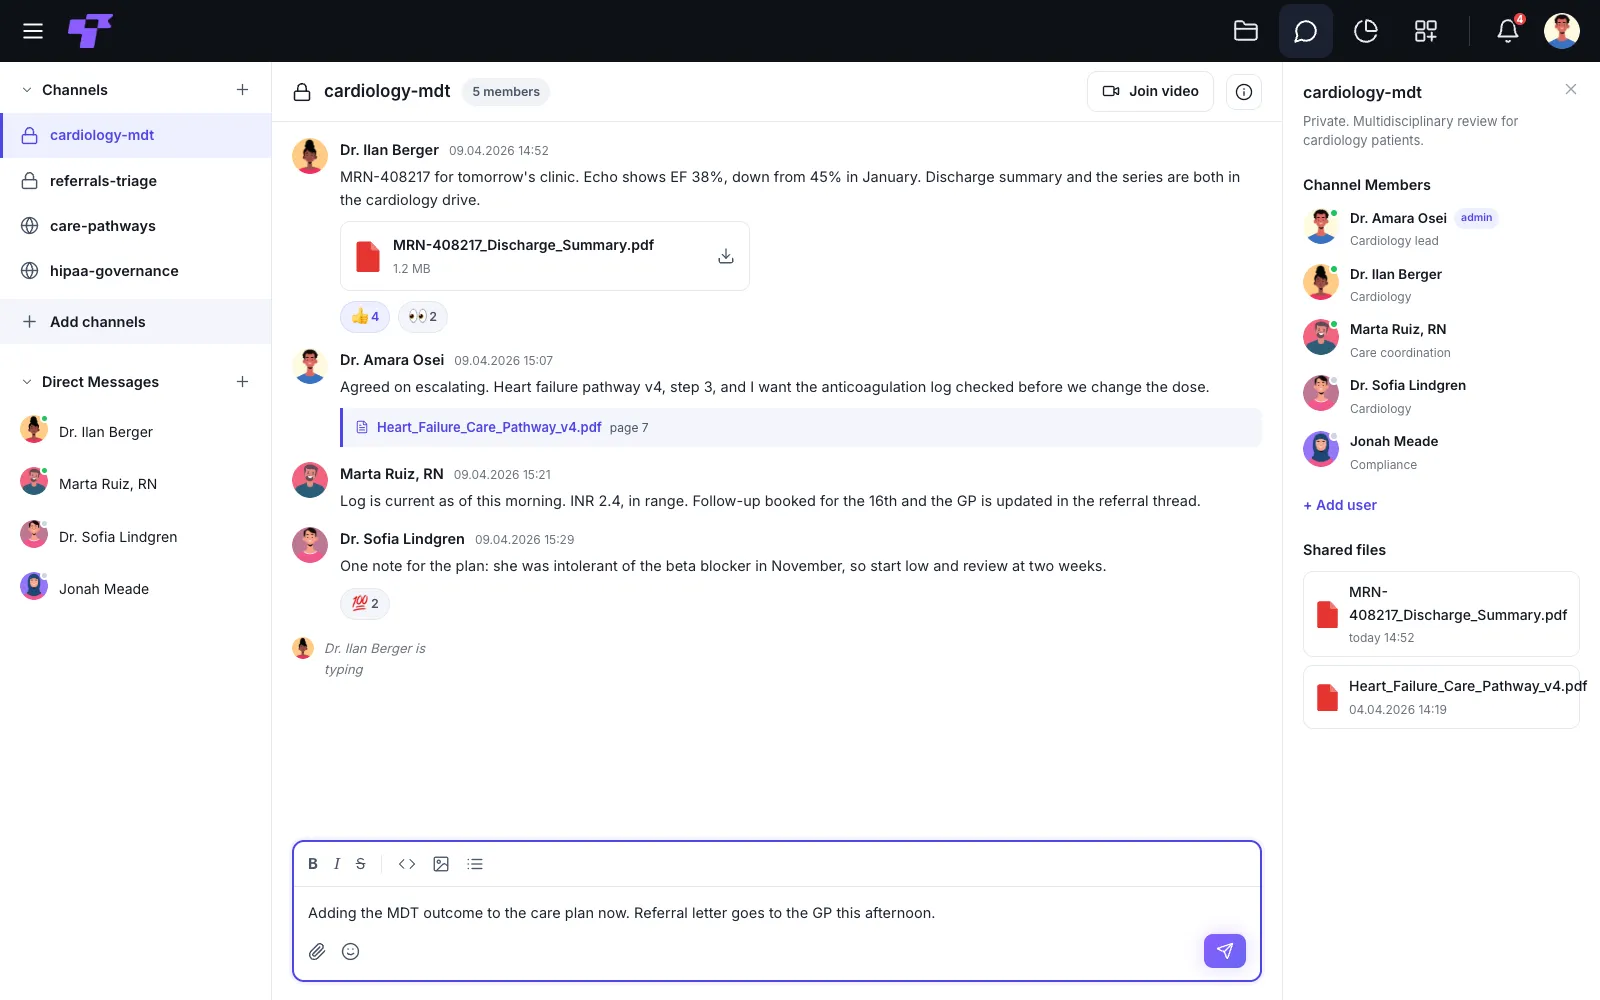
A team of specialists reviews a case with the discharge summary and care pathway linked inline, so every decision points back to its clinical source.
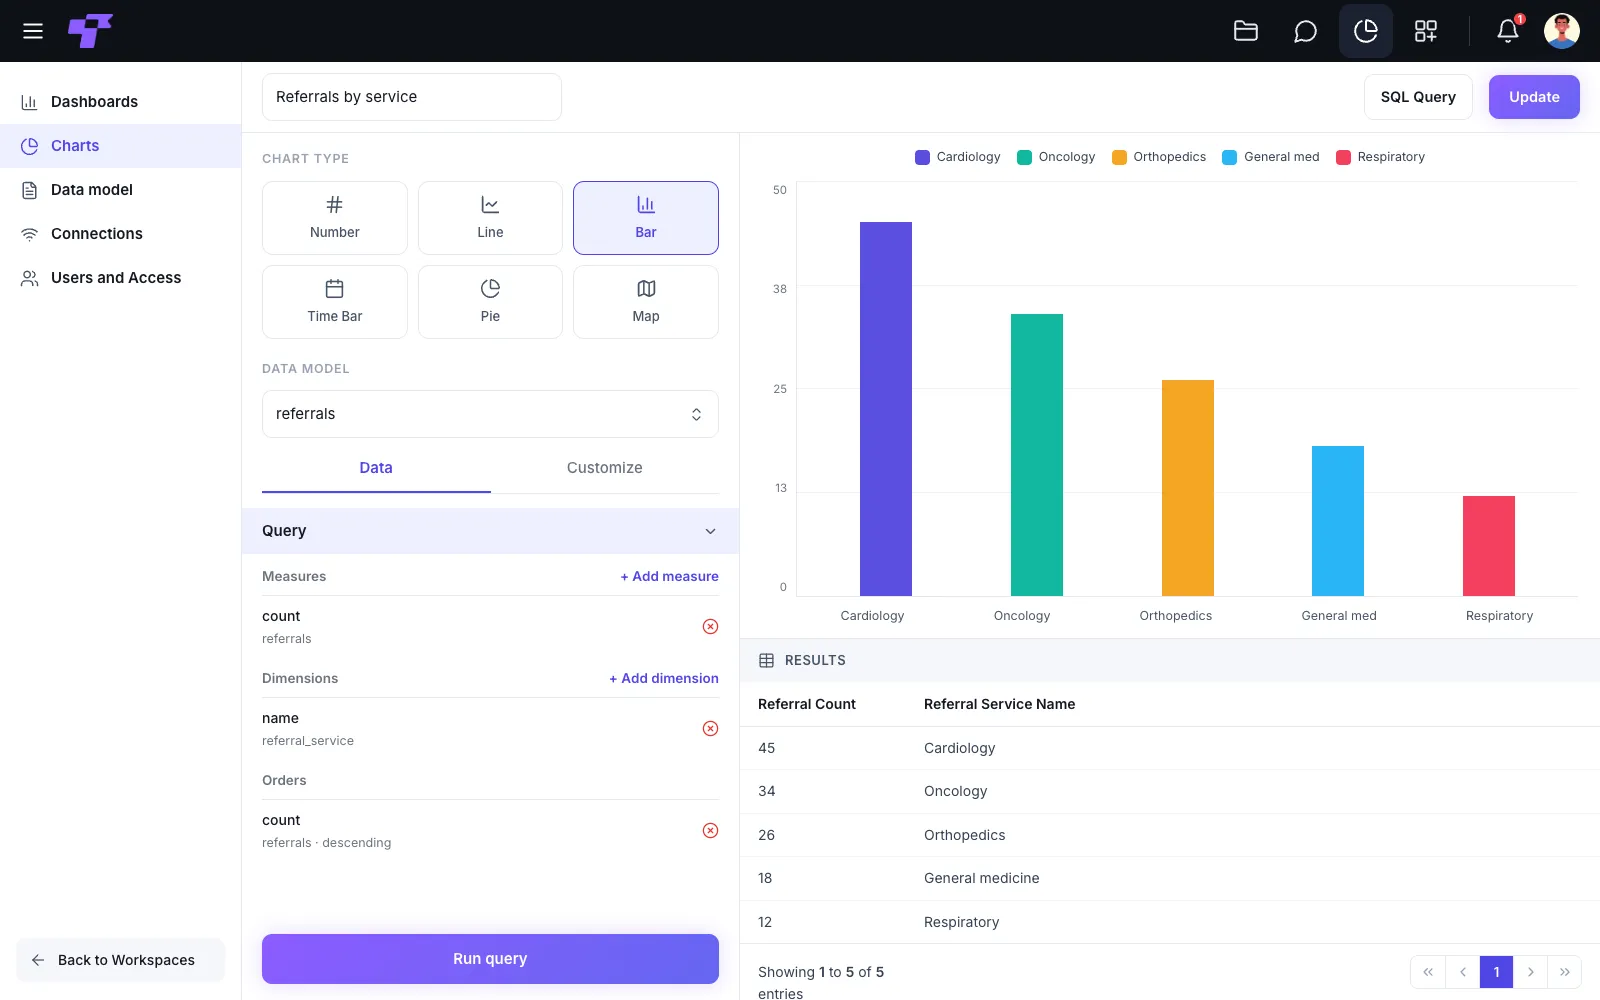
Department leads see referral volume across services from the same data, without exporting patient records into a separate reporting tool.
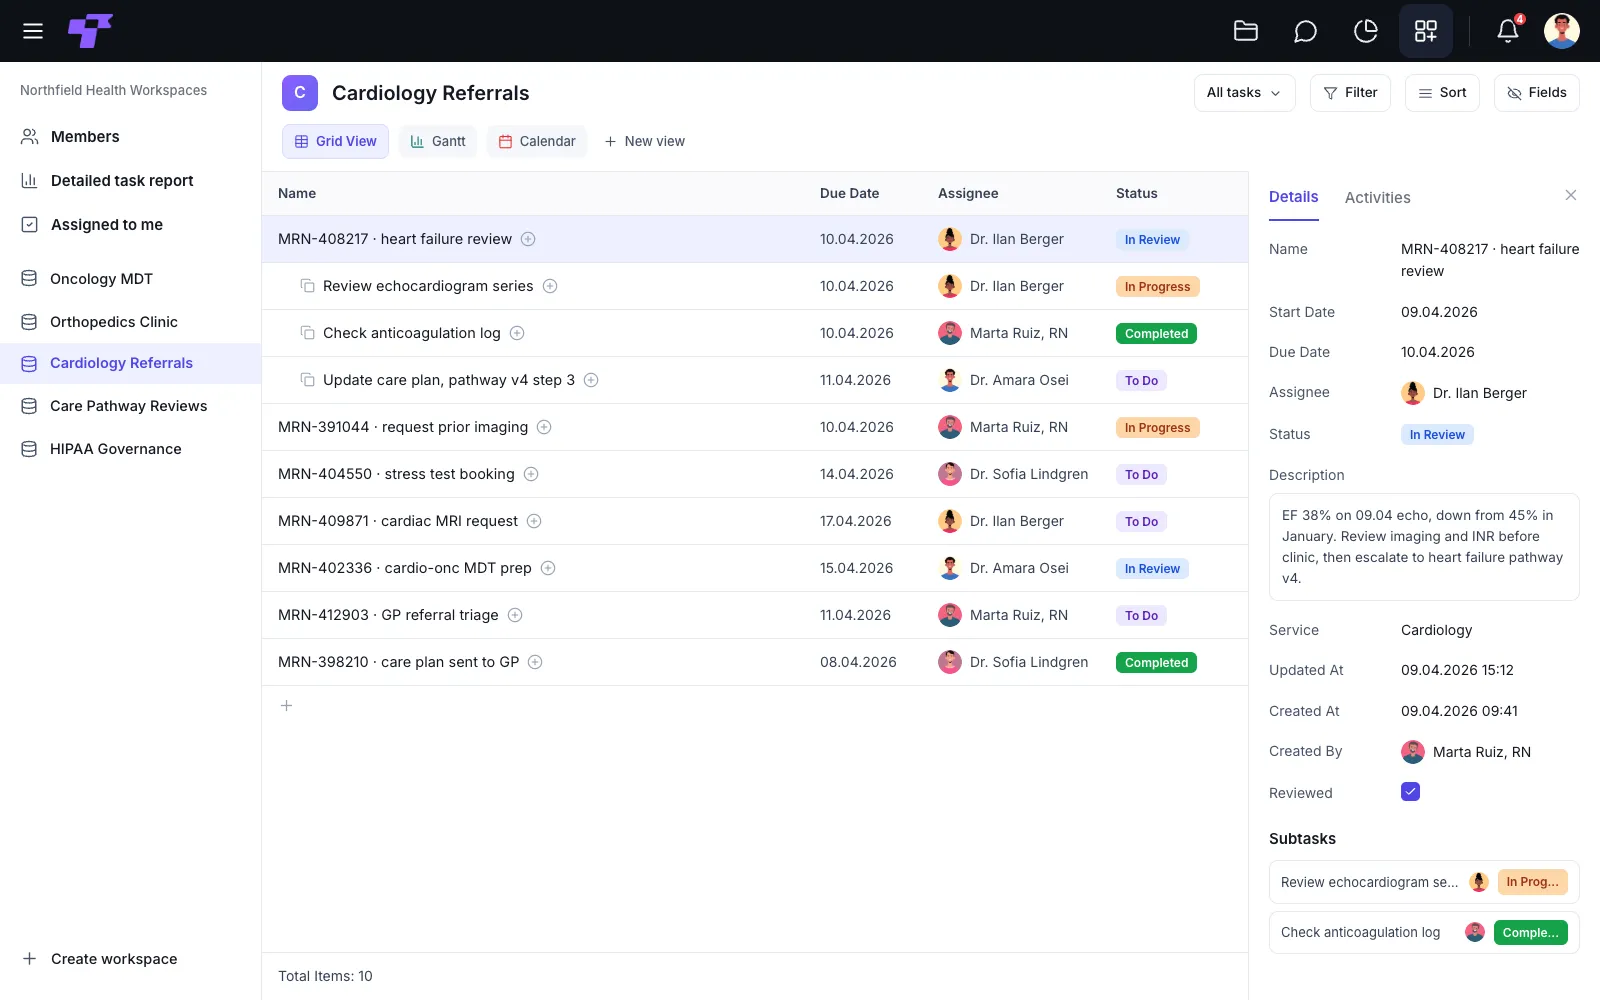
Every referral, subtask, and sign-off is tracked on one board, so a heart failure review never stalls waiting on an email reply.
Patient-data control is not a compliance checkbox. It is the difference between AI clinicians can actually trust at the point of care and AI they have to work around.
Here's how Twigex fixes it.
See it working in your sector.
Talk to our team about your specific compliance requirements and deployment constraints.